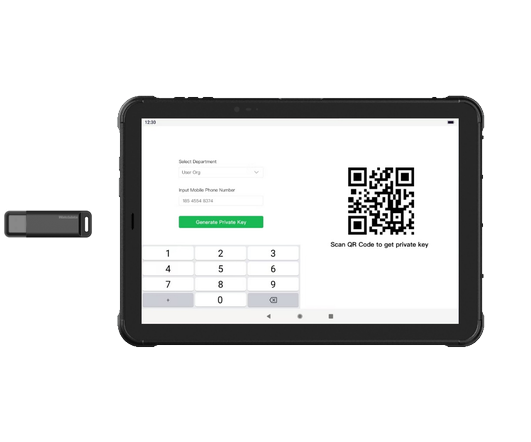
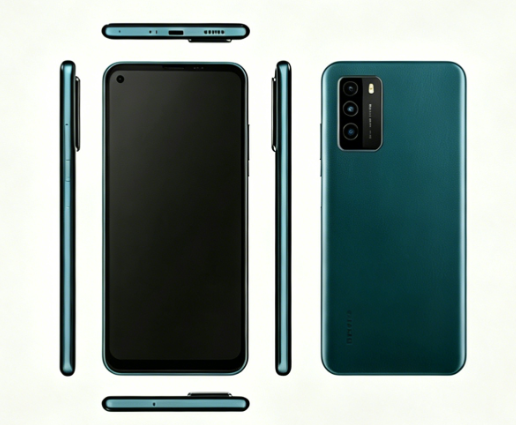
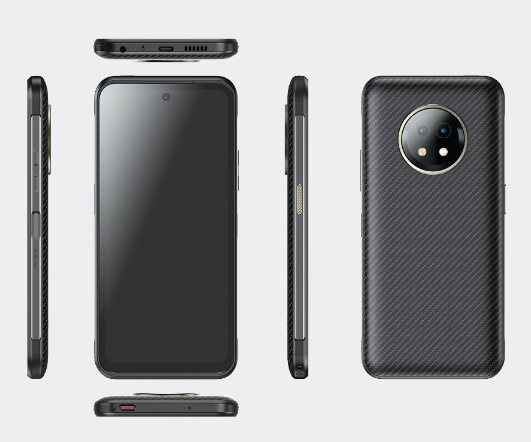
KMS, F70, D51 devices with specifications and package pricing
View Details →
🔒
Solution Principles
Technical architecture, encryption algorithms and key system design
View Details →
💬
FAQ
Frequently asked questions covering general, business and technical topics
View Details →
☎
Contact Us
Get in touch for inquiries, demos, partnerships and technical support
View Details →
Solution Overview
How our VoLTE encryption solution works
SIM/eSIM Card
Provided by the carrier, VoLTE service must be enabled.
KMS
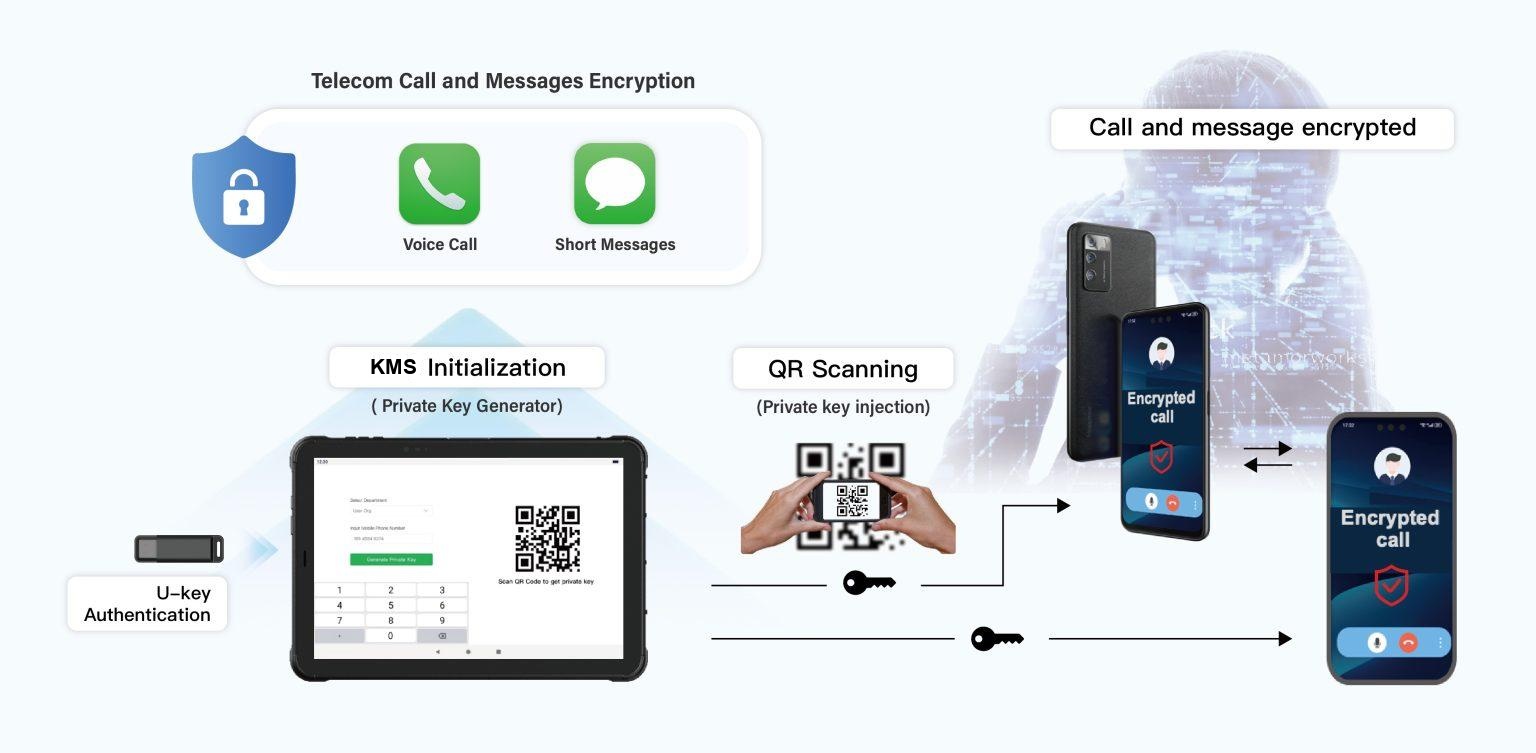
Provided by us with U-key. It manages the root key, generates user keys for each communication number, and distributes them to terminals via scanned QR codes.
5G VoLTE Encryption Phone
Provided by us, with multiple models available for selection. Based on the Unisoc chipset’s VoLTE interface authorization, deep customization at the modem and phone communication software levels.
We provide the VoLTE encryption call solution without any support and detecting from carriers, avoiding the interception from carrier’s network or 3-party attackers. You only need normal SIM cards to make encrypted calls, directly use the carrier’s VoLTE service without deploying any server.
Product Lineup
Three core devices working together for complete encrypted communication
Key Management
KMS
Offline key management system with U-key secure storage
Key technical advantages of our VoLTE encryption architecture
🔑
Build Your Own Key System
Possess your own KMS root key to build the trust root for your encryption system, eliminating concerns about communication interception by device manufacturers.
🔗
IBE Key Exchange
SAKKE/ECCSI identity-based encryption enables unidirectional key exchange. No online KMS needed during calls — lighter, more secure, no single point of failure.
🔒
TEE Secure Storage
User private keys encrypted via Trusted Execution Environment. Even if the phone is stolen, attacker can only obtain encrypted keys — cracking requires breaching TEE.